RecoverYantraSuite on the command line
Every command this product contains and every parameter it accepts: 39 commands, 199 parameters. Read from the shipping build, version 7.8.10.76. The help text says what a switch does; each entry here adds when a business reaches for it and what it costs.
Before the first command
- Reading a physical drive needs administrator rights. Working from a disk image needs none.
- The source is opened read-only for the whole session, and the application refuses a destination on the drive being read.
- Set the mode before the scan. A recovery-mode scan does not become evidential afterwards.
- Everything below is available in the application as well; the command line is the scriptable surface, not a separate product.
recoveryantra acquire
-o | Folder to write the image into (default: ./Evidence) When to use it. Point this at the evidence store for the case, not at the machine's own disk. On a booted rescue USB the default writes to the stick itself, which is usually what you want in the field. What it costs. The folder must have room for the whole source. The pre-flight refuses rather than filling the disk half way through. |
|---|---|
--retries | Retries for bad sectors (default 3) When to use it. Raise it when the drive is readable but marginal and the case justifies a slow, thorough pass. Lower it to 0 or 1 when the drive is deteriorating and getting a complete-enough image quickly matters more than the last few sectors. What it costs. Every retry is another read of a failing surface. On a drive that is physically degrading, high retry counts can cost you the areas you have not reached yet. |
--force | Start even if the pre-flight checks object. When to use it. Only when you have read the pre-flight objection and know it is wrong for your situation, for example free space reported incorrectly by a network share. What it costs. The pre-flight exists to stop a job that cannot finish. Forcing past a genuine space or same-drive objection loses work, and on the same-drive case it can overwrite the very data being recovered. |
--write-block | Engage a SOFTWARE write-block (OS read-only) on the source first. Best-effort and not a substitute for a hardware write blocker; layered with the fingerprint. When to use it. Use on every evidential acquisition where no hardware write blocker is available. It sets the operating system's own read-only flag on the source before the first read. What it costs. It is best effort at the operating-system level and is not equivalent to a hardware write blocker. State which one you used in the report; do not describe a software block as a hardware one. |
--format | Image format: raw (.img, resumable) or E01. Asked for when omitted. When to use it. raw when the image will be recovered from or examined on the same bench and a stopped copy must be resumable (the .map carries on); e01 when it goes to a lab that expects Expert Witness containers or when the destination is smaller than the drive and compression has to make it fit. Asked for on screen when omitted. What it costs. An E01 copy cannot be resumed part way; a raw copy takes the drive's full size on the destination. |
--boot | On the RecoverYantra bootable USB: offer the USB's own DATA partition and any other attached drive as the destination, never the drive being copied or the boot medium; record the read-only protection. When to use it. Set by the RecoverYantra bootable USB's own launcher: the USB's DATA partition is offered first as the destination, then any other attached drive that is neither the source nor the boot medium, and the manifest records that every disk arrived read-only. What it costs. Outside the bootable USB there is no live medium, so the flag is ignored with a note and -o decides where the image goes. |
--operator | Examiner asserting lawful authority (recorded) When to use it. Record the individual asserting lawful authority for the acquisition. Required practice for anything that may be produced in proceedings. |
--authority | Lawful basis: warrant / consent / statutory power When to use it. Record the lawful basis: warrant, consent, or a statutory power. Write what it actually is, and keep the underlying document with the case file. What it costs. This field records the assertion. It is not legal advice and it does not create authority you do not have. |
--org | Examiner's organisation (recorded) When to use it. The examining organisation, as it should appear on the report and in the custody record. |
--case | Case / FIR reference (recorded) When to use it. Your own case or FIR reference. Set it at acquisition so every later artefact carries the same identifier. What it costs. Adding it afterwards means the earliest records in the trail carry a different reference from the rest. |
recoveryantra audit
<path> | Path to audit_trail.jsonl (or the folder holding it) When to use it. Run at the close of a case, and again before disclosure, against the audit_trail.jsonl produced during the work. It proves the trail has not been edited, reordered or had entries inserted. |
|---|---|
--manifest | A recovery_manifest.json holding the sealed receipt, so entries REMOVED from the trail are detected too When to use it. Add the recovery manifest whenever you need to prove nothing was REMOVED from the end of the trail. The manifest holds the sealed receipt the chain alone cannot see past. What it costs. Without it, a trail that has been cut short at the end still verifies. For evidential work treat the manifest as required. |
recoveryantra batch
<batch_cmd> | When to use it. Queue several drives to image and/or recover, then run them in sequence with nobody watching. `new` starts a batch; `add` queues a job on it; `list`/`status` show its progress; `remove`/`move` edit the queue before it runs; `start`/`resume` run it; `pause`/`stop` are typed in another window while it is running; `report` writes what happened across the whole batch. Use it when there are more drives on the bench than there is time to sit and watch each one. |
|---|
recoveryantra bootusb
--target | The mounted USB (e.g. E:\ on Windows, /media/usb on Linux) When to use it. The mounted rescue USB. Use when you need to carry the tool to a machine that must not be written to or cannot be dismantled. What it costs. Existing files on the stick are left alone, but confirm you have chosen the stick and not an external evidence drive. |
|---|---|
--tool | Path to RecoverYantra-cli.exe to copy onto the USB (defaults to this executable) When to use it. Point at a specific build when preparing a stick for a machine that must run a version you have already validated for the case. |
--payload-iso | A live Linux ISO, to make the USB bootable When to use it. Supply a live Linux ISO when the target machine will not start, so the stick can boot it and read the drive in place. What it costs. Writing an ISO makes the stick bootable and ERASES it. Check the ISO carries a USB boot record first, or the stick will be written perfectly and still not boot. |
--payload-dir | An extracted WinPE / live-Linux tree, to make it bootable When to use it. Use an extracted WinPE or live-Linux tree instead of an ISO when your organisation maintains its own validated boot environment. |
recoveryantra capabilities
--enable | Turn on an advanced method (e.g. checkm8, mtk_bootrom, qualcomm_edl) When to use it. Turn on an advanced acquisition method for a case that needs it and is authorised for it. These methods interact with the device, so they are off until an examiner opts in on the record. What it costs. Enabling is recorded in the audit trail with the operator and case. An advanced method can alter the device; decide before the exhibit is in front of you, not during. |
|---|---|
--disable | Turn an advanced method back off When to use it. Turn a method back off once the step that needed it is complete, so the next case starts from the conservative default. |
--tools | Show the acquisition toolbox: the public methods (checkm8/mtkclient/edl/adb...), what's installed, and what is equipped for this case When to use it. Run before an acquisition to see which external tools are actually installed on this machine and which methods are therefore available today. What it costs. The product orchestrates the operator's own tools for advanced methods; it does not bundle exploits. A method with no tool present is not available however the case is authorised. |
--operator | Examiner making the choice (recorded) When to use it. Name the examiner making the decision. The choice belongs in the record alongside the result it produced. |
--case | Case reference (recorded) When to use it. Tie the capability decision to the case it was made for. |
recoveryantra case
<case_cmd> | When to use it. Group several recovered sources - a laptop disk, a backup stick, a phone image - into one case for a single customer or job, and see everything recovered across them in one place, deduplicated by hash. `new` starts a case; `add` puts a source into it; `list` shows the cases or one case's sources; `status` totals its files and duplicates; `dedup` lists files found in more than one source. Use it when a job is more than one drive and you do not want to hand back the same file three times. |
|---|
recoveryantra cctv
--device | Recorder disk (e.g. \\.\PhysicalDrive2 or /dev/sdb) When to use it. Point at the recorder's disk when you have the disk itself and the recorder is unavailable or its export function is broken. What it costs. Reading a recorder disk directly is read-only, but the recorder must be powered down and the disk removed. A running recorder overwrites the oldest footage continuously. |
|---|---|
--image | Image of the recorder disk (.dd/.img/.e01) When to use it. Preferred over --device for any matter that may be produced. Image the recorder disk once, then work from the image. |
-o | Where to write recovered clips (required when scanning a disk/image) When to use it. A folder on the case store with room for the clips. Recorder disks are large and footage recovers as many separate files. |
--min-clip | Ignore fragments smaller than this many bytes (default 65536) When to use it. Raise it when a sweep is returning large numbers of very short fragments and the incident you care about is minutes long. Lower it when the event of interest is only a few seconds. What it costs. Raising the floor discards short fragments permanently for that run. If the incident may be brief, run low first and filter afterwards. |
--max-clips | Stop after N clips When to use it. Cap the run when you are sampling a large recorder to establish what is on it before committing to a full extraction. What it costs. A capped run is not a complete extraction. Say so in the notes, and do not report the cap as the total footage present. |
--identify-only | Just report which recorder this disk is, don't extract When to use it. Run first on any unfamiliar recorder disk. It reports which recorder wrote the disk without extracting anything, which tells you how long the real job will take and whether the format is supported. |
--force | Start even when the pre-flight checks say this cannot finish: too little room, or writing onto the drive being recovered. When to use it. Only after reading the objection. See the same switch on acquire. What it costs. Forcing past a same-drive objection can overwrite the footage you are extracting. |
<cccmd> | When to use it. Read the recorder's camera index, play a clip's timeline, list a scan's clips, download or cut one out, extract several, enhance a frame or a range, capture a frame pack, or build a media report. Every subcommand is documented on its own line. |
recoveryantra check
--device | Raw device path (e.g. \\.\PhysicalDrive1 or /dev/sdb) When to use it. Run the feasibility check the moment a drive arrives, before quoting, before imaging and before any promise to the client: it measures how much of the drive is unreadable and states the chances in plain words. What it costs. A few hundred sampled reads - seconds on a healthy drive, and one gentle attempt per area on a failing one. Far cheaper than discovering mid-copy that the job was never viable. |
|---|---|
--image | An existing image file to check instead When to use it. Check an existing image instead of a drive - for example to confirm a copy received from a client or another lab reads cleanly before work is billed against it. |
--pdf | Also write the answer as a PDF report at this path When to use it. Write the verdict as a PDF wherever a client, insurer or case file needs the answer on record. The report states its numbers as ranges and says it is based on a sample. |
--samples | How many areas of the drive to test (default 160) When to use it. More samples narrow the stated range and cost more reads of the drive. The default suits a first assessment; raise it when the estimate must be tighter than a few percent. What it costs. Each extra sample is another read of a drive that may be dying. On clearly failing hardware, keep the default and move to the copy. |
recoveryantra cloud
<cloudcmd> | When to use it. Pick what to do: `steps` shows the stages (free); `ingest` takes in a provider export the admin produced; `collect` acquires a mailbox live over the API; `caches` finds local sync caches. |
|---|
recoveryantra compare
<scan_a> | Scan A: a session id from the history, or a recovery output folder When to use it. The FIRST scan - a session id from the history, or the path to a recovery output folder. Normally the earlier pass, so that what the second scan added reads as the gain. |
|---|---|
<scan_b> | Scan B: the re-scan / deeper scan, same kind of reference When to use it. The SECOND scan of the same source - the re-scan, the deeper scan, or the one run after a settings change. Files only in this scan are what it added, which is usually the reason for comparing at all. What it costs. Comparing is read-only and charges nothing: it reads what the two scans already wrote. Files are matched by EXACT SHA-256 - a file with the same NAME but different bytes is reported in its own bucket and is never called the same file, because a deleted name can survive while the space under it is reused. |
--export | Write the diff to this folder (scan_compare.csv/.json) When to use it. Write the comparison into this folder - scan_compare.csv or .json - so the four buckets go into a job sheet or a report rather than staying on screen. The folder is created if it is not there. |
--format | Export format (default csv) When to use it. csv (the default) writes one row per file occurrence, so a changed file appears twice with its A side and its B side and the sheet opens in Excel; json writes the whole comparison for a script. |
recoveryantra db
--identify | Identify a database file and print its recovery method When to use it. Run this first on any database file. It names the engine and the recovery method that applies, which decides whether this is a ten-minute job or a specialist one. |
|---|---|
--coverage | List every database family we cover and the recovery tier When to use it. Use when quoting or scoping. It lists every database family the build covers and the tier of recovery available for each. What it costs. A family listed at identify-and-route tier is not row-level recovery. Quote against the tier, not the presence in the list. |
--recover | Recover records from a database file (dBase/.dbf built; others are identified and routed to their method) When to use it. Point at a copy of the data file when the server will not start or will not attach it, and the most recent backup is unusable. What it costs. Work from a COPY. Take the instance offline first: extracting from files a running engine is writing to produces rows from a moment that never existed as a consistent state. |
--memo | With --recover of a .dbf: the memo side-file (.dbt/.fpt) When to use it. Required with a dBASE .dbf whose text fields live in a side file. Without it the long text fields come back empty. |
--out | With --recover: write all records (deleted marked) to a CSV When to use it. Write to CSV whenever the rows are going to be reviewed, handed to a client, or loaded into a working server. What it costs. Deleted rows are exported flagged. Preserve that column: an un-flagged export presents recovered deleted rows as live data. |
recoveryantra detect
--report | Also write the report (HTML, PDF, JSON) into DIR When to use it. Write the detection report - HTML, PDF and JSON - into this folder: every device with its state, bus, serial and sector size, the hardware Windows can see but cannot use with the code and the fix, and the Plug-and-Play inventory. Use it when a customer or a partner says a drive is not detected: the report replaces "it does not work" with what the machine actually sees. What it costs. The folder goes through the same pre-flight as every other writing job; the report is small, so only rights and a full disk stop it. |
|---|---|
--no-health | Skip the health read of each usable drive (faster) When to use it. Skip the health read of each usable drive. Detection is then a listing only and returns in a second or two. Use it on a machine with many drives, or when a drive is known to be failing and you do not want even a test read against it before imaging. |
--force | Write the report even if the pre-flight objects When to use it. Write the report even when the pre-flight objects to the folder. Use it only when you have read the objection and it does not apply - a report is a few hundred kilobytes, so the usual reason is a destination the check cannot judge. What it costs. A refusal you have not read is not one you can override safely. |
recoveryantra distribute
<distcmd> | When to use it. Pick what to do: `plan` shows how the work would split and what it refuses without needing nodes; `node` runs a worker that searches byte ranges; `carve` coordinates a distributed carve and writes the files here. |
|---|
recoveryantra ecryptfs
<tree> | A folder of recovered eCryptfs files (encrypted ECRYPTFS_FNEK_ENCRYPTED.* names and/or eCryptfs bodies) When to use it. Point at the folder of recovered eCryptfs files - an Ubuntu encrypted home or a Synology encrypted share pulled off the disk. Every encrypted filename and file body under it is decrypted with the passphrase you give. |
|---|---|
--passphrase | The eCryptfs MOUNT passphrase (not the login password, unless the two are the same) When to use it. The eCryptfs MOUNT passphrase, which is what unwraps the file keys. On Ubuntu it is usually NOT the login password: it is the long passphrase that ecryptfs-unwrap-passphrase prints at setup. What it costs. A file or filename this passphrase does not unlock is reported and left encrypted, never handed back as invented plaintext, so a wrong passphrase costs nothing and produces nothing. |
-o | Where to write the decrypted tree When to use it. Where to write the decrypted tree. Choose a folder off the source drive; the decrypted files are written under their recovered folder structure with their real names restored. |
--force | Write even if the pre-flight objects When to use it. Write the decrypted tree even when the pre-flight objects, for example when free space is tight at the destination. Use it only after reading the warning. What it costs. The pre-flight is what stops a half-written output; forcing past it can leave a partially decrypted tree behind. |
recoveryantra erase
<target> | Device to erase (e.g. \\.\PhysicalDrive2) When to use it. The drive being retired. Used when storage is leaving the organisation and a record of its sanitisation has to be retained. What it costs. This is the one command in the product that destroys data. The system drive, the drive the product runs from and the drive holding the report are refused outright. |
|---|---|
--confirm | The drive's own serial number (or its size in bytes if it reports none). Required - nothing is erased without it. When to use it. Type the drive's own serial number. This is the step that prevents erasing the wrong disk. What it costs. There is no override. If the drive reports no serial, its size in bytes is used instead. |
--passes | Overwrite passes (default 1 - NIST SP 800-88 Rev. 1) When to use it. Leave at 1. NIST SP 800-88 Rev. 1 is explicit that a single overwrite pass is sufficient on modern media. Raise it only where an internal policy or a contract demands a specific number. What it costs. Additional passes multiply the time on a large drive and add no measurable security. Do not cite them as stronger sanitisation. |
--pattern | Fill pattern (default zero - the only one that can be verified afterwards) When to use it. Leave at zero. A zeroed drive can be PROVEN clean by reading it back; random fill cannot be distinguished from data that was already encrypted. What it costs. Choosing random makes the verification pass weaker, not stronger, and a carve over random data produces false candidates. |
--out | Folder for the certificate and audit trail When to use it. The folder for the certificate and audit trail. Put it on the records store, not on the drive being erased. |
--examiner | Name recorded on the certificate When to use it. The name that appears on the certificate. Use the person accountable for the disposal, as your policy defines it. |
--firmware | Also issue the drive's OWN firmware sanitize (NIST 'Purge': ATA/NVMe Sanitize or crypto-erase) where the drive supports it. Certified as Purge only when the drive confirms completion. When to use it. Add this to reach NIST Purge on drives that support it. The drive's own controller sanitises areas an overwrite cannot address, including remapped and spare blocks on flash. What it costs. Only used where the drive genuinely supports it; the certificate records the level ACHIEVED, not the level requested. A firmware sanitise on some drives is not interruptible. |
--purge-method | Force a firmware method instead of the strongest the drive supports (with --firmware) When to use it. Force a specific firmware method when your policy names one, or when the strongest method the drive advertises is known to be unreliable on that model. What it costs. Forcing a weaker method than the drive supports lowers the level reached, and the certificate will say so. |
--no-verify | Skip reading the drive back and trying to recover from it When to use it. Only for a bulk pass over drives that will be physically destroyed afterwards anyway, where the verification time is not justified. What it costs. Skipping verification removes the entire basis for the certificate's central claim. Do not issue an unverified certificate to a client or an auditor as though it were verified. |
recoveryantra find-drive
<pattern> | A filename, part of one, or a wildcard (e.g. IMG_2019, *.jpg) When to use it. Search every usable attached device for a file whose name matches PATTERN, without picking a drive first. Free, no licence needed - reads each device's index in seconds, the same tier as `--list`. Use it when the customer cannot say which of several drives holds what they want. |
|---|---|
--timeout | Give up on one drive after this long (default 20); a slow or failing drive never holds up the others When to use it. Seconds allowed per device before moving on. A slow or failing device costs only its own row - the sweep never waits on one device at the expense of the rest. |
--all | List every drive checked, including the ones with no match When to use it. Also sweep devices that are not in a normally-usable state, where possible. Use it only once the plain sweep has come back empty. |
recoveryantra fixvideos
<folder> | Folder holding the recovered videos When to use it. Run over a completed recovery folder when videos are listed as recovered but will not play. It repairs the index in the recovered COPY. What it costs. It cannot restore picture data that was overwritten on the source. A clip whose media was partly lost stays partly lost. |
|---|
recoveryantra fixwith
--file | The damaged file to repair When to use it. The damaged clip or photograph. Use when a file recovered without its index or its tables and will not open. |
|---|---|
--reference | A healthy file from the same camera or phone When to use it. A healthy file from the SAME camera or phone, ideally the same settings. The reference donates structure only. What it costs. A reference from a different device produces a file that opens and is wrong. Picture data is never taken from the reference, and the repaired file contains only the damaged file's own frames. |
-o | Where to write the repaired copy (default: alongside the damaged file) When to use it. Write the repaired copy to the case store when the original has to be preserved exactly as recovered. |
recoveryantra gui
--classic | Use the classic Tkinter wizard When to use it. Fall back to the classic interface on a machine where the modern window will not start, typically an old or minimal Windows install. |
|---|
recoveryantra guide
--html | Write the guide as a self-contained, searchable HTML page When to use it. Produce the manual as a single searchable page to hand to a client, put on an internal share, or carry onto an air-gapped bench. |
|---|---|
--markdown | Write the guide as Markdown When to use it. Produce Markdown when the content is going into your own documentation system or version control. |
recoveryantra hpa
--device | The physical drive (e.g. \\.\PhysicalDrive2). Must be a direct SATA connection - USB bridges do not pass ATA When to use it. The physical drive to measure or reveal, as a device path. It must be a DIRECT SATA connection: USB bridges and virtual disks do not pass the ATA commands a Host Protected Area is measured with. |
|---|---|
--reveal | Actually lift the HPA and image the hidden sectors (needs -o and --confirm-serial); without it, only measure When to use it. Actually lift the Host Protected Area and image what it hid, instead of only measuring. This is one of the four operations in the whole product that WRITE to a drive, so it is deliberate and confirmed. What it costs. It sends a volatile SET MAX ADDRESS to the drive to expose the hidden sectors, images them, then restores the original limit - and restores it even if the run is interrupted. The drive is briefly changed on purpose; a DCO, if present, is measured but never removed. |
-o | Where to write the image of the hidden area (with --reveal) When to use it. Where to write the image of the revealed hidden area. Choose a folder on another drive; the hidden sectors, their map and a hashed manifest are written there. |
--confirm-serial | Type the drive's own serial number back to confirm the target (with --reveal) When to use it. Type the target drive's own serial number back, exactly, to confirm you mean this drive before anything is written to it. The reveal is refused until it matches. What it costs. This is the guard against revealing the wrong drive: a write to a drive's ATA limits is not something to do to the wrong one, so the serial must match what the drive reports. |
--examiner | Recorded in the audit trail (with --reveal) When to use it. A name recorded in the audit trail for the reveal, so the record says who performed it. It is written into the manifest, not onto the drive. |
--force | Write the image even if the pre-flight objects When to use it. Write the image of the hidden area even when the pre-flight objects, for example over tight free space at the destination. Use it only after reading the warning. What it costs. The pre-flight is what stops a half-written image of the hidden area; forcing past it can leave the imaging incomplete even though the HPA is still correctly restored. |
recoveryantra image
--device | Raw device path (e.g. \\.\PhysicalDrive1 or /dev/sdb) When to use it. Image the drive first whenever it is failing, whenever the original must go back to the client untouched, or whenever the matter may be produced. Every later step runs against the image. What it costs. Imaging reads the whole drive once. On a drive that is actively dying that single pass is the best chance you get, so choose the retry policy before starting, not after. |
|---|---|
--source | Existing image/file to re-image When to use it. Re-image an existing file, for example to convert a raw image to E01 or to make a working copy of an evidence image. |
-o | Output image path (.img or .E01) When to use it. The image path on the case store. Name it for the exhibit, not for the machine. |
--retries | Retries for bad sectors (default 3) When to use it. Same trade-off as on acquire: more retries recover more marginal sectors and cost more reads of a failing surface. |
--format | raw .dd/.img (default) or compressed .E01 evidence image When to use it. Use e01 for evidential work: it is compressed and carries the acquisition metadata other forensic tools expect. Use raw when the image will be mounted or read by tooling that only takes a flat image. What it costs. Raw images are the size of the whole drive, including empty space. |
--targeted | Filesystem-aware (read-once): image only the space the filesystems say holds data, skipping free space without reading it. Faster and gentler on a failing drive, and a smaller image. Deleted files still in free space are NOT captured - use a full image for those. When to use it. Filesystem-aware, read-once imaging: the filesystems' own allocation maps say which space holds data, and only that is read and copied - free space is skipped without touching the drive. Use it to image a large or failing drive faster and more gently, and to get a smaller image, when the live files are what matter. What it costs. Deleted files still sitting in free space are NOT captured - free space is exactly where they live. When deleted data matters, take a full image (omit --targeted). A filesystem we cannot read a map for is imaged in full, so it is never wrong, only sometimes not smaller. |
--entropy-map | Measure the entropy of the data as it is copied and record which spans are high-entropy (encrypted or compressed) in the image's .map.json. When to use it. Measure the entropy of the data as it is copied and record which spans are high-entropy - encrypted or compressed - in the image's .map.json. Use it to see at a glance whether a drive (or a region) is encrypted before spending time on recovery. What it costs. Entropy cannot tell encryption from compression; a high-entropy span may be either. It is a signpost, not a verdict. |
--force | Start even when the pre-flight checks say this cannot finish: too little room, or writing onto the drive being recovered. When to use it. Only after reading the objection. See acquire. |
recoveryantra legal
--status | Show what has been acknowledged on this install When to use it. Show what lawful-use acknowledgements have been made on this install. Useful when auditing a shared bench machine. |
|---|---|
--reset | Forget remembered acknowledgements (history is kept) When to use it. Clear the remembered acknowledgements when a machine changes hands or a new operator takes it over. What it costs. The history is retained. Resetting does not erase the record of what was previously acknowledged. |
recoveryantra list
--triage | Also check each device's health (SMART + test reads), how it's connected, and what kind of device it is (CCTV recorder, phone, dashcam, card, ...) with advice on what to do When to use it. Run before touching anything. It reports each device's health, how it is connected and what kind of device it is, which is what decides whether to recover directly or image first. What it costs. Triage reads the drive. On a drive that is audibly failing, keep even this brief and go straight to imaging. |
|---|
recoveryantra mail
<path> | The .pst / .ost / mbox / Maildir / .eml to read When to use it. Point at the mail store itself, including one the mail client refuses to open. Take a copy first and work from the copy. |
|---|---|
-o | Folder to write recovered messages into When to use it. Where the exported messages go. Never the folder holding the store being read. |
--list | List what is in the mailbox without exporting it When to use it. Run first. It shows what is in the mailbox, and whether the store read cleanly or had to be salvaged, before you commit to a full export. What it costs. A salvaged read recovers messages but may not recover the folder structure. Knowing which you have changes what you promise. |
--format | eml = one file per message (drag into Outlook); mbox = one file (Thunderbird, Apple Mail, converters) When to use it. Choose eml when the messages are going back into Outlook or being reviewed individually; each message is a separate file. Choose mbox when the mailbox is going into Thunderbird, Apple Mail or a review platform as a single container. What it costs. Neither format is a .pst. The product extracts messages; it does not rebuild an Outlook store file. |
recoveryantra nandrecon
<dump> | The raw NAND dump from the lab (spare areas included) When to use it. The raw dump a lab read straight off the bare NAND chip, spare (OOB) areas included. It is not a disk image yet; this command is what turns it into one the recovery engine can read. |
|---|---|
-o | Where to write the reconstructed image When to use it. Where to write the reconstructed image, on a different drive from the dump. The rebuilt image is written whole so the ordinary recovery flow can open it like any other disk image. |
--analyse | Report the geometry / scrambling / ECC / block-map findings and write nothing - run this first When to use it. Read the dump and report the geometry, scrambling, error correction and block map it can work out, writing nothing. Run this first, before you commit to an image, because it costs nothing and tells you which figures still need supplying. |
--page-size | Page size in bytes, if the lab told you When to use it. The page size in bytes when the lab already measured it, so it is taken as fact instead of inferred. Supplying a wrong figure produces an image that looks like a disk and holds nobody's files, so give it only when you know it. |
--spare-size | Spare (OOB) size in bytes, if known When to use it. The spare (out-of-band) area size in bytes when the lab measured it. It is taken as given rather than inferred; a wrong value shifts every page and the result carves to nothing, so supply it only when known. |
--pages-per-block | Pages per block, if known When to use it. How many pages make up an erase block when the lab measured it. It is used for the block map; an image can still be built without it, in the order the chip stores rather than logical order. |
--xor-key | The lab's XOR de-scramble key file, if they have one When to use it. A file holding the controller's XOR keystream when the lab supplied one. A dump scrambled from end to end cannot be de-scrambled by analysis alone, so this file is what makes such a dump readable at all. |
--xor-period | The repeating XOR period in bytes, if known When to use it. The length in bytes at which the scrambling keystream repeats, when it is known. It narrows the de-scramble search; leave it off and the period is recovered from the dump. |
--ecc-scheme | The controller's ECC scheme, if detection failed When to use it. The controller's error-correction code, bch or hamming, when automatic detection could not settle it. It decides how spare bytes are read as correction data, so name it only when you know the controller. |
--ecc-step | ECC data step size in bytes When to use it. How many data bytes each error-correction step covers, when detection needs help. It pairs with the scheme and strength; the wrong step corrects nothing, so supply it only from the controller's datasheet. |
--ecc-t | ECC strength (correctable bits per step) When to use it. The correction strength, the number of bit errors each step can fix, when detection needs help. It has to match the controller; a value too low leaves errors, too high reads correction bytes as data. |
--ecc-offset | Offset of the ECC bytes in the spare area When to use it. Where the correction bytes begin inside each page's spare area, when it is known. It positions the read of the correction data; leave it off and the offset is inferred from the dump. |
--ftl-offset | Offset of the block-address field in the spare area When to use it. Where the logical block address sits inside the spare area, when the lab knows the controller. It is what lets the blocks be put back into the order a filesystem expects rather than the chip's own order. |
--ftl-width | Width of the block-address field in bytes When to use it. How many bytes the logical block-address field takes in the spare area, when it is known. It pairs with the offset to read the block map; an image still builds without it in physical order. |
--ftl-endian | Byte order of the block-address field When to use it. The byte order of the block-address field, little or big, when the lab knows the controller. It only matters once the offset and width are set, and the wrong order scrambles the block map. |
--force | Write an image even when the geometry is not confident (the result may be nonsense that looks like a disk) When to use it. Write an image even when the geometry could not be confirmed, taking the best guess rather than refusing. Use it only after --analyse shows how uncertain the figures are. What it costs. A forced image is built on unconfirmed page and block sizes, so it can look like a sound disk while holding nonsense; the run records that it was forced. |
recoveryantra raid
--members | Member images in array order; use '-' for a missing member When to use it. List the member images IN ARRAY ORDER. Use a dash for a member that is missing or has failed. What it costs. Order matters. Getting it wrong produces a volume that looks plausible and contains scrambled files, which is worse than an obvious failure. |
|---|---|
--auto | Read the geometry from the members' md superblocks (Linux/NAS) instead of giving --level/--chunk When to use it. Try this first. It reads the geometry from the members' own metadata, which removes the guesswork on Linux, NAS, Intel RST and Windows dynamic disks. What it costs. Auto-detection needs the metadata to survive. Where it does not, fall back to stating the level and chunk size yourself. |
--level | RAID level when not --auto: 0, 1, 4, 5, 6, 1e, 10, 50, 60, jbod When to use it. State the level when the metadata is gone and you know the array's configuration from documentation or the controller. |
--chunk | Stripe/chunk size in bytes (default 65536) When to use it. State the stripe size with --level. It is the single value most often recorded wrongly in site documentation. What it costs. A wrong chunk size assembles an array that mounts and returns corrupt files. Verify by checking that recovered files open. |
--layout | RAID5/6 parity layout (default left-symmetric) When to use it. Change from the default only for an array documented as using a different parity layout. |
--list-volumes | List the volumes these disks hold and stop (Windows dynamic disks can carry several) When to use it. Run first on Windows dynamic disks. One set of disks can carry several volumes, and you need to know which one holds the data. |
--volume | Which volume to recover on Windows dynamic disks, by the name Windows gave it (e.g. Volume1) When to use it. Select the volume by the name Windows gave it, from --list-volumes. |
-o | Folder to write recovered files When to use it. The output folder, on separate storage from the member images. |
--mode | Recovery mode (smart/fs/carve) When to use it. As on recover: smart unless you have a reason. On a reassembled array, smart is almost always right because the file system is usually intact once the geometry is correct. |
--sector-size | When to use it. Change from 512 only for arrays built on 4K-native drives, where leaving it wrong prevents the volume being found at all. |
--include-intact | When to use it. Add when you need the whole volume out, not only what was deleted. This is the normal case for a failed array: nothing was deleted, the array stopped assembling. |
recoveryantra ransomware
--dir | Folder of encrypted files + ransom notes to examine When to use it. Point at a folder holding encrypted files and the ransom note. The first question in every incident is which strain, because that decides what is realistically recoverable. |
|---|---|
--names | Observed filenames (encrypted files and/or note files) When to use it. Supply observed filenames when you cannot give the tool access to the affected system, for example when working from a photograph of a screen or a client's email. |
--note-file | Ransom-note text file(s) to read When to use it. Supply the ransom note itself. It is often the strongest single identifier of the family. |
--list | List the known ransomware families and their outlook When to use it. Review the known families and their outlook when scoping an incident or briefing a client on likely outcomes. |
--decryptor | Show the offline decryptor index for a family: the legitimate tool, publisher, LE-key status, flaw time-box and scope - or that no decryptor exists When to use it. Check whether a legitimate published decryptor exists for the identified family before planning any other recovery. What it costs. Where none exists the index says so. Do not substitute an unverified tool found by searching; that is how a second incident starts. |
--verify-tool | With --decryptor FAMILY: SHA-256 a downloaded decryptor and check it against the catalog (or print the hash to compare against the publisher) When to use it. Always run this against a decryptor you have downloaded, before running it on client data. What it costs. A decryptor obtained from anywhere other than the named publisher is an unknown executable being run against the only copy of the data. |
--triage | Damage-assessment triage of a folder of hit files: how many are recoverable with no key, salvageable, or truly encrypted - before any decryption is attempted When to use it. Run early. It reports how many files are recoverable with no key, how many are salvageable, and how many are genuinely encrypted, before anyone commits to a recovery plan or a payment discussion. |
--recover-originals | Find the decryption-free ORIGINALS the ransomware left behind (temp/autosave/backup, Recycle Bin, cloud caches, DB WAL sidecars) and pair them to the encrypted files When to use it. Run on every incident. Many strains write a new encrypted file and delete the original; those deleted originals are frequently still present in free space, temp folders, the Recycle Bin, cloud caches and database sidecar files. What it costs. This is the highest-value step in the whole flow and it is time-critical: continued use of the machine overwrites exactly the free space the originals are sitting in. |
--usnjrnl | With --recover-originals: a $UsnJrnl:$J blob to resurrect what was deleted/hit, with paths When to use it. Add the change journal to --recover-originals when you need the original PATHS as well as the file contents. |
--verdict | The full ransomware flow over a folder: triage + identify + recover-originals, fused into one honest recovery verdict (tier + prioritised action plan) When to use it. The single command to run when you need one defensible answer for a client or an insurer: triage, identification and originals recovery fused into a stated outcome with a priority order. |
--memory | With --verdict: a memory image / pagefile to scan for the key (aeskeyfind / rsakeyfind) When to use it. Supply a memory image or pagefile with --verdict when the machine was captured while still running. Some strains leave key material in memory. What it costs. This only helps if memory was captured before shutdown. It is a reason to capture memory first at the scene. |
--esxi | ESXi/Linux recovery playbook for a strain (esxiargs, blackbasta_esxi, lockbit_linux): flat-VMDK descriptor rebuild, intermittent-encryption damage map, keystream reuse When to use it. Use for a hypervisor or Linux estate rather than a workstation. It produces the playbook for that family: descriptor rebuild, damage mapping, and what the specific strain leaves recoverable. |
--rebuild-vmdk | Rebuild a VMDK descriptor for an intact <name>-flat.vmdk; needs --flat-size BYTES When to use it. Use when the flat VMDK holding the virtual machine's data survived but its small descriptor file was encrypted. Rebuilding the descriptor makes the intact data readable again. What it costs. Requires the exact byte size of the flat file. A wrong size produces a descriptor that opens and misreads the disk. |
--flat-size | Exact byte size of the -flat.vmdk (with --rebuild-vmdk) When to use it. The exact size in bytes of the -flat.vmdk, taken from the file itself, not from the datastore listing. |
--nas-snapshots | Enumerate NAS (QNAP/Synology/LVM) snapshots from a file of LVM2 metadata text - the pre-attack recovery sources When to use it. Enumerate NAS snapshots from the volume metadata. On QNAP, Synology and LVM estates these are frequently the fastest complete recovery and are missed because the attacker deleted the visible backups. |
--lotl | Living-off-the-land recovery: scan recovered scripts, registry exports and memory strings (a file or folder) for the BitLocker recovery key or archive password that abuse of BitLocker/EFS/7-Zip left behind. The secret is often still there, not an exfiltrated RSA key, so a ShrinkLocker case is not 'AES, unrecoverable' When to use it. Scan recovered scripts, registry exports and memory strings for the recovery key or archive password that living-off-the-land ransomware left behind when it abused BitLocker, EFS or a bundled 7-Zip. The secret is often still present, so a ShrinkLocker case is not the unrecoverable AES it first looks like. What it costs. It recovers the key the abuse left, it does not break BitLocker or strong archive crypto; a case with no left-behind key is reported as such rather than pretended recoverable. |
--reconstruct | Rebuild a document (Office/PDF) or media file from an INTERMITTENTLY-encrypted copy: recover the readable content the ransomware left between its encrypted blocks (R3b) When to use it. Point at one INTERMITTENTLY-encrypted file - a document or a photo the ransomware only part-encrypted to save time. It pulls back the readable content left in the intact blocks between the encrypted ones. Use it when a large file is 'damaged' rather than fully scrambled. What it costs. This is surviving content, not a decryption: the parts that WERE encrypted are still gone, so the result can be partial. It is written only when something readable is actually found. |
--exploit | Attempt a DOCUMENTED cryptographic weakness on an encrypted file - keystream reuse / repeating-key XOR - and write the plaintext only if it validates (R4) When to use it. Point at one encrypted file to attempt a DOCUMENTED cryptographic weakness - a reused or repeating keystream, which some families leave. Use it when identification flags keystream reuse; it does nothing against a sound per-file key, and says so. What it costs. The recovery is a heuristic and is accepted only when it validates as no-longer-ciphertext, so a wrong key is refused rather than written. Always confirm the recovered file opens before relying on it. |
--period | With --exploit: the keystream period in bytes if it is known (0 detects it) When to use it. The keystream length in bytes, when you already know it from the family or from analysis; leave it at 0 to let the tool detect the period from the repeats in the ciphertext. |
--out | Where to write the recovered file (with --reconstruct or --exploit); without it, the result is only reported When to use it. Where to write the reconstructed or recovered file. Choose a path off the affected drive; without it the result is only reported, not saved, so nothing is written until you ask for it. |
recoveryantra recover
--device | Raw device path (e.g. \\.\PhysicalDrive1 or /dev/sdb) When to use it. Recover directly from the attached drive when it is healthy, the job is not evidential, and time matters. What it costs. If the drive is failing, image it first. A direct scan reads the whole surface and can be the read that finishes a dying drive. |
|---|---|
--image | Disk image file (.dd/.img/.iso) When to use it. The default choice for anything evidential, anything failing, and anything where the original must be returned untouched. |
--ios-backup | An iOS (iTunes/Finder) backup folder (Manifest.db) When to use it. Point at an iTunes or Finder backup folder when the handset itself is unavailable, locked, or must not be touched. |
--slabmap | Storage Spaces slab-map JSON: reassemble a pool virtual disk from member images and recover from it When to use it. Reassemble a Storage Spaces virtual disk from member images and recover from the assembled volume. |
-o | Output directory for recovered files (required unless --list) When to use it. Always a separate drive from the source. The product refuses a destination on the drive being read. |
--mode | smart=metadata+carving (default), fs=named files only, carve=signatures only When to use it. Leave at smart. It parses the file system for original names and folders AND carves free space for what the metadata no longer covers. Use fs when you want named files quickly from an intact file system; use carve on formatted or badly damaged media where the metadata is gone. What it costs. fs alone misses everything the file system no longer indexes. carve alone returns files without their original names or folders. smart is what maximises the result. |
--resume | Carry on from where an earlier scan of the same source into the same output folder stopped, instead of starting again from the beginning When to use it. Continue a scan that was stopped, on the same source into the same output folder. A large drive is an overnight job and does not need to be restarted. What it costs. The checkpoint belongs to the DRIVE, not the path. A different disk in the same slot restarts from the beginning, with the reason stated. |
--include-intact | Also recover currently-existing (non-deleted) files When to use it. Add whenever the loss is a volume rather than a deletion: a reformatted disk, a RAW volume, a failed array. In those cases the files were never deleted and the default deleted-only view will look almost empty. What it costs. It substantially increases the output size, because it recovers everything present as well as everything deleted. |
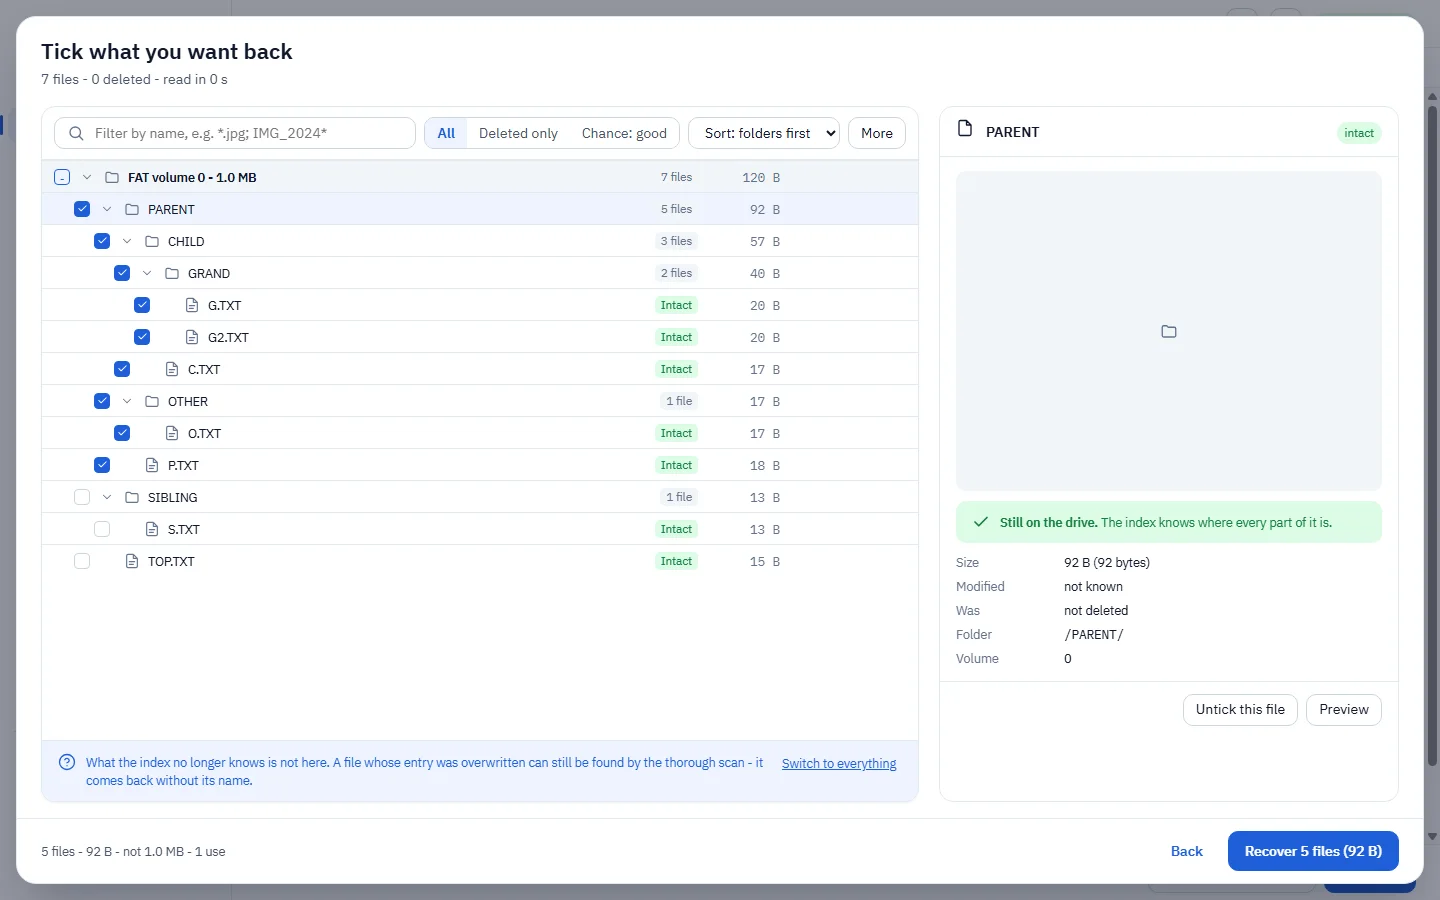
--list | Print the drive's folder tree from its index (live and deleted files) and stop. Fast; nothing is written. -o is not needed. When to use it. Look before you scan. Reads the filesystem index only and prints the folder tree - live and deleted files, deleted ones marked - in seconds, writing nothing. Use it first on any drive whose index is intact: it tells you whether the folder the customer wants is still named, so you can recover that alone with --only instead of reading the whole drive. What it costs. Free, and needs no licence. What it cannot show is anything whose index entry is gone - a formatted card, a wiped table - which still needs the full scan. |
--only | Recover only this folder or file (repeatable). Paths are the volume's own, e.g. --only /Users/jo/Documents/ --only /Photos/IMG_0042.jpg. Implies --mode fs and --include-intact. When to use it. Recover one folder or file rather than everything: the customer wants the Documents folder, not four hours and a terabyte of working folder. Repeat the switch for several paths; a folder path takes everything under it, and 1:/Folder/ names the folder on partition 1 only. Paths are the volume's own, as --list prints them. What it costs. Implies --mode fs and --include-intact. Every content check, the manifest and the organising run exactly as in a full scan; a use is still charged for the drive. |
--engine | native=built-in (default), photorec=use TestDisk's PhotoRec, auto=PhotoRec if installed When to use it. Leave at native. Select photorec only to cross-check a result with a second implementation, which is occasionally useful in a disputed matter. What it costs. The external engine must be installed separately and does not carry this product's validation or its verdicts. |
--workers | Carving processes: 0=auto/all cores (default, byte-identical output, ~3x faster), 1=single-threaded, N=that many When to use it. Leave at 0 so the carve uses the available cores. Set 1 when you need the machine responsive for other work, or when reproducing a result exactly for a report. What it costs. Output is byte-identical either way; only the time changes. Below about 128 MB the product stays single-threaded because process start-up costs more than it saves. |
--sector-size | Bytes per sector (default 512) When to use it. Change from 512 only for 4K-native drives, where the wrong value prevents the volume being recognised. |
--password | Unlock an encrypted drive. A BitLocker 48-digit recovery password, a LUKS passphrase, or a key in hexadecimal. When to use it. Supply the BitLocker recovery password, LUKS passphrase or hex key for an encrypted volume. What it costs. Without the correct credential the volume cannot be read by anyone. The product states that rather than returning fragments. The credential is not retained for a later resume. |
--force | Start even when the pre-flight checks say this cannot finish: too little room, or writing onto the drive being recovered. When to use it. Only when you have read the pre-flight objection and established that it is wrong for your situation. What it costs. The two objections it can override are both serious: too little room means the scan stops part way, and writing onto the drive being recovered overwrites the data you are trying to get back. |
--report | Generate a recovery report after scanning (comma-separated: pdf,docx,html; default all) When to use it. Generate the report at the end of the scan whenever the result goes to somebody else: a client, an insurer, or a case file. |
--profile | Override the mode for this run (forensic=hash+manifest+evidence, recovery=fast+by-type). Defaults to the saved global mode. When to use it. Override the saved mode for this one run, for example a single evidential job on a bench normally used for commercial recovery. What it costs. Setting it per run avoids the more common error, which is leaving a bench in forensic mode and hashing every file on high-volume commercial work. |
--apfs-snapshots | List the APFS snapshots on the source (point-in-time views that may hold deleted/overwritten files) and stop When to use it. Run first on any Mac volume. Snapshots are point-in-time views that often still hold the file as it was before it was deleted or overwritten. |
--apfs-snapshot | Recover files as they were in this named APFS snapshot (byte-exact from the copy-on-write extents) When to use it. Recover from the named snapshot. Where the file exists in a snapshot, this returns it byte-exact and is far better than carving for it. |
--vss-list | List the Windows Volume Shadow Copies on the source (previous versions - originals from before deletion or ransomware) and stop When to use it. Run first on any Windows volume, and always in a ransomware incident. Shadow copies hold previous versions from before the deletion or the encryption. |
--vss-snapshot | Recover files as they were in this shadow copy: the snapshot-time volume is reconstructed and scanned When to use it. Reconstruct the volume as it was at that snapshot and recover from it. This is frequently the fastest complete recovery available. |
recoveryantra remote
<rcmd> | When to use it. Work with a machine across the network. `agent` runs on the far machine and offers its disks read-only; `discover` and `list` find it and show what it has; `image` copies a disk that is not in use; `volumes` asks a running machine what it has and whether it can be frozen; `live` acquires a machine that is STILL IN USE, through a snapshot taken on that machine. Use the network route when the drive cannot be removed: a machine under warranty, a server that cannot be opened, a member of staff three time zones away, or a site you cannot attend. What it costs. The transfer is only as reliable as the link. The image is verified on arrival, and a short image is reported failed rather than handed over as complete. `live` additionally creates a snapshot on the far machine, which allocates space there - so a live acquisition writes to the endpoint even though it never writes to the data being acquired, and every result records that. A volume that cannot be frozen is refused rather than read while it moves. Live acquisition is built into Enterprise, Forensics and the Suite. |
|---|
recoveryantra search
<dir> | A recovery output folder that has a search_index.db/json When to use it. A completed recovery folder. Use when the recovery produced more files than anyone can review by eye. |
|---|---|
<query> | Keywords (phrase in quotes, prefix*, AND/OR/NOT allowed) When to use it. Search by keyword, phrase in quotes, prefix with an asterisk, or a combination with AND, OR and NOT. |
--category | Limit to a category When to use it. Narrow to photographs, documents and so on when you know the shape of what you are looking for. |
--state | Limit to a state (recovered/deleted) When to use it. Separate files that were deleted from files that were present. In a dispute, which of the two a document was found in is often the point. |
--limit | Max results When to use it. Raise it when the default cap is hiding results you need. What it costs. The full-text half of the index is bounded on very large recoveries. The product says when it is; do not read an empty result as proof of absence without checking that. |
recoveryantra steps
<workflow> | Workflow id (e.g. forensics, data_recovery); omit to list them by category When to use it. Show the full procedure for one job - every stage, what it is for, the safety gates that cannot be skipped, and the command that carries each one out. Use it when a technician is doing a job for the first time, when a job is done rarely enough that nobody remembers the order, or when a reviewer asks why the work was done the way it was. |
|---|---|
--category | Show only one category's workflows When to use it. Show only data recovery, or only forensics. The two follow different orders because they are for different things: a recovery is judged on how much comes back, an examination on whether you can prove what you did. Verification therefore ends a recovery and sits in the MIDDLE of an examination, before any analysis. Use this to hand a new examiner only the sequence that applies to them. |
--commands | Print only the commands, in order, ready to copy When to use it. Print only the commands, in order, ready to paste. Use it to build a runbook, to script a job that is done the same way every time, or to check a script somebody else wrote actually follows the procedure. |
--standards | Show the published practice each step comes from When to use it. Show the published practice each stage comes from - ISO/IEC 27037, NIST SP 800-86, the ACPO principles. Use it when a client, an auditor or a court asks why a step exists, and when training staff who need to know the procedure is not this vendor's opinion. |
recoveryantra timemachine
--device | Disk to read (e.g. \\.\PhysicalDrive2) When to use it. Read a Time Machine backup disk directly when you need files from a Mac that is unavailable. What it costs. A Time Machine backup is built from hard links. Reading it without resolving them returns correctly named, empty stubs. |
|---|---|
--image | Disk image to read When to use it. Preferred: image the backup disk and read the image. |
--offset | Byte offset of the volume (default: find it) When to use it. Give the volume offset only when it cannot be found automatically, typically on a damaged partition table. |
recoveryantra unlock
<system_dir> | The image's /data/system folder (holding gesture.key / password.key / locksettings.db) When to use it. Point at the /data/system folder from an Android image when the device credential is needed and you are authorised to recover it. What it costs. This works on an IMAGE you have already lawfully acquired. It is not a way into a handset you cannot already read. |
|---|---|
--wordlist | Optional word list for a non-numeric password When to use it. Supply a word list when the credential is a password rather than a numeric PIN. |
--max-pin | Longest PIN to try (default 6; raising it costs time) When to use it. Raise beyond 6 only when the case justifies the additional time, which grows sharply with each digit. |
--operator | Examiner asserting lawful authority (recorded) When to use it. The examiner asserting lawful authority. |
--authority | Lawful basis: warrant / consent / statutory power When to use it. The lawful basis. This step in particular should never be run without one recorded. |
--org | Examiner's organisation (recorded) When to use it. The examining organisation, recorded against a step that in most jurisdictions will be examined closely if the matter is contested. |
--case | Case / FIR reference (recorded) When to use it. The case reference, so this step appears in the same custody record as the acquisition it was run against. |
recoveryantra validate
<groups> | Which groups to run (DFR CARV WB AUD IMG SS); default all When to use it. Run the shipping engine against known ground truth. Do this on a new bench, after an upgrade, and on a schedule your quality process sets. What it costs. This is modelled on the NIST CFTT specifications. It is not a NIST certification and the report says so; describe it accurately. |
|---|---|
--out | Folder to write validation_report_<time>.json/.txt into When to use it. Write the dated validation report to the quality records store. |
--federated | Also print/write a NIST-Federated-Testing-styled conformance report (test cases grouped by FT tool category; modelled on CFTT FT, not NIST-issued) When to use it. Add the Federated-Testing-styled conformance report when your accreditation or client requires test cases grouped by tool category. |
recoveryantra veracrypt
<container> | Volume file or image (a raw device path also works) When to use it. A VeraCrypt or TrueCrypt volume file, or a device path. Use when the data is inside an encrypted container and the password is lawfully available. |
|---|---|
--password | Volume password (omit to be prompted, so it is not left in shell history) When to use it. Omit it to be prompted. Typing a password on the command line leaves it in shell history and in process listings. What it costs. On a shared or logged bench, treat the prompt as the only acceptable route. |
--pim | Personal Iterations Multiplier (0 = VeraCrypt default) When to use it. Supply the Personal Iterations Multiplier if the volume was created with one. Without the correct value the correct password still fails. |
--cipher | Restrict to one cipher/cascade (e.g. AES, Serpent, AES-Twofish-Serpent). Omit to try all. When to use it. Restrict to one cipher when it is known, which cuts the unlock time considerably. What it costs. Restricting to the wrong cipher makes a correct password look wrong. |
--prf | Restrict to one PRF (sha512/sha256/blake2s/whirlpool/streebog). Omit to try the usable ones. When to use it. Restrict the hash function when it is known, for the same reason. |
--truecrypt | Treat as a legacy TrueCrypt volume (different iteration counts and TRUE magic) When to use it. Set for a legacy TrueCrypt volume; the iteration counts and the header magic differ. |
--hidden | Unlock the hidden volume (header at offset 65536) When to use it. Unlock the hidden volume rather than the outer one, where a hidden volume exists and you are authorised to access it. |
--json | Also write the structured result (no key material) here When to use it. Write the structured result for the case file. No key material is written. |
recoveryantra which
<situation> | What is happening, in plain words (e.g. "drive is clicking"); omit to list every situation When to use it. Describe what is happening in your own words - "drive is clicking", "formatted the wrong disk", "Outlook will not open it" - and get the feature to use, why that one rather than the obvious alternative, a worked example, the commands, and what NOT to do. Use it when somebody hands you a job and you are not sure which part of the product it belongs to, and give it to new staff before you give them anything else. |
|---|---|
--all | Show every situation, grouped, rather than searching When to use it. List every situation, grouped, instead of searching. Use it to see the whole range at once - useful when scoping what a product will cover for a customer, and for training. What it costs. Situations the product you are running does not include are marked, so the list stays honest about what this build can actually do. |
recoveryantra wipe
<folder> | Folder to sanitise When to use it. Sanitise the working folder at the end of a job, so a client's recovered data does not sit on the bench indefinitely. What it costs. On flash, copy-on-write file systems and anything that has been backed up, overwriting a folder does not guarantee every copy is gone. The limits are stated every time. |
|---|---|
--passes | Overwrite passes (default 1 - NIST SP 800-88 Rev. 1) When to use it. Leave at 1. As on erase, more passes cost time and add nothing measurable. |
--yes | Do not ask for confirmation When to use it. For scripted end-of-job cleanup only, where the folder is chosen by the script and not by a person. What it costs. Removing the confirmation removes the last check that the right folder was named. |
recoveryantra wizard
<name> | Workflow id (e.g. data_recovery); omit to list them When to use it. Print the guided steps for a workflow. Useful for a new operator, or for a procedure your team runs rarely enough to want the sequence in front of them. |
|---|---|
--list | List the available guided workflows When to use it. List the guided workflows available in this product. |