Acquire, analyse, report
A recovery engine and a forensic toolkit in one product. It images read-only, hashes every acquired and exported item, keeps a hash-chained audit trail, and produces a report that carries the method and the evidence alongside the conclusion.
Every stage leaves a record.
Write-blocked imaging
Image any source to E01 or raw dd, source read-only and fingerprinted before and after.
Verified hashing
SHA-256 on every acquired and exported file, recorded in a manifest.
Hash-chained audit
Every action commits to the one before it; the trail names the first break.
Chain of custody
The source offset of every recovered file: which sectors of the exhibit this is.
OS artefacts
Recycle Bin, USN, prefetch, registry, LNK, event logs, ShellBags, AmCache, plus macOS.
Memory forensics
Credentials, keys and process artefacts from a RAM capture.
Mobile acquisition
Android and iOS, logical and, in our lab, physical and rooted, with deleted records.
CFTT-style validation
The shipping engine run against known ground truth, in a dated report. Not a NIST accreditation, and we say so.
Nothing unaccounted for.
A recovered file carries its SHA-256, its source offset, and the mode it was recovered in. The audit trail is hash-chained, so a single edited line is caught.
Acquire
Write-blocked image, hashed on the way in, source verified unchanged over the regions a stray write would touch.
Analyse
Recover, carve and pull artefacts from the image, never the original, every result traced to a source offset.
Attest
A dated report in PDF, Word or HTML, with the hash-chained trail sealed so truncation is caught too.
The honest line
Modelled on the NIST CFTT method and says so. A rigorous self-validation, not a NIST accreditation.
Put us next to the best.
Capability by capability, against the tools a lab would otherwise buy.
Acquisition
Getting the evidence off the device, intact.
| Capability | SakshyaYantra Forensic SuiteThis suite + lab | OpenText EnCaseForensic platform | Magnet AXIOMForensic platform | Exterro FTKForensic platform | AmpedVideo forensics |
|---|---|---|---|---|---|
| Write-blocked imaging with hashing | Yes | Yes | Yes | Yes | No |
| Evidence containers (E01, AFF4, raw) | Yes+ AFF4 | YesE01 is theirs | Yes | Yes | No |
| Damaged-media imaging (retry, skip map) | Yes | Partial | Partial | Partial | No |
| Mobile acquisition (logical to full file system) | Yes+ licensed frontier | Partialadd-on | Yes | Partial | No |
| Network / remote acquisition | Yes | Partialadd-on | YesCyber | PartialEnterprise | No |
Examination and analysis
What you can find once it is acquired.
| Capability | SakshyaYantra Forensic SuiteThis suite + lab | OpenText EnCaseForensic platform | Magnet AXIOMForensic platform | Exterro FTKForensic platform | AmpedVideo forensics |
|---|---|---|---|---|---|
| Windows / macOS / Linux artefacts | Yes | Yes | Yes | Yes | No |
| Memory (RAM) analysis | Yes | Yes | Yes | Partial | No |
| Combined timeline across artefacts | Yes | Yes | YesTimeline | Yes | No |
| Full-text index and search | Yes | Yes | Yes | Yesvery fast | No |
| Encrypted volume decryption | YesBitLocker, LUKS, FileVault, VeraCrypt | Yes | Yes | YesPRTK | No |
| Known-file hash sets (NSRL / KFF) | Yes | Yes | Yes | YesKFF | No |
Video forensics
The recorder, the picture, and whether it can be trusted - Amped's ground.
| Capability | SakshyaYantra Forensic SuiteThis suite + lab | OpenText EnCaseForensic platform | Magnet AXIOMForensic platform | Exterro FTKForensic platform | AmpedVideo forensics |
|---|---|---|---|---|---|
| Recorder / DVR footage recovery and conversion | Yes | No | Partialseparate | No | YesDVRConv + Engine |
| Enhancement with the chain shown, and measurement | Yes | No | No | No | YesFIVE |
| Authenticity, tamper and camera identification | Yes | No | No | No | YesAuthenticate |
| Number-plate assistance | Yes | No | No | No | YesDeepPlate |
| Three times never merged (PTS, overlay, case) | Yes | No | No | No | Partialoverlay |
| Frame pack as the evidence-transfer unit | Yes | No | No | No | No |
Evidence handling and reporting
What survives scrutiny afterwards.
| Capability | SakshyaYantra Forensic SuiteThis suite + lab | OpenText EnCaseForensic platform | Magnet AXIOMForensic platform | Exterro FTKForensic platform | AmpedVideo forensics |
|---|---|---|---|---|---|
| Chain-of-custody reports | Yes | Yes | Yes | Yes | Yesvideo reports |
| Hash-chained tamper-evident audit trail | Yes | Partiallogging | Partial | Partial | Partialproject |
| Per-item hash AND source offset in the report | Yes | Partial | Partial | Partial | Partial |
| S.63(4) BSA 2023 evidence certificate | Yes | No | No | No | No |
OpenText EnCase
An established forensic platform; E01 is its format. EnScript automation, deep artefact work, memory and a manual RAID rebuild. Mobile is a separately licensed add-on; no video-forensic line.
Magnet AXIOM
Magnet.AI categorisation, Timeline and Connections, and wide cloud and app artefact coverage. Built for post-acquisition analysis; DVR/CCTV is a separate product.
Exterro FTK
Distributed processing over multi-terabyte sets, PRTK decryption, KFF known-file filtering and strong email handling. Built for scale; no video-forensic suite.
Amped
The video-forensic line: FIVE (restore, enhance, measure), Authenticate, Replay, DVRConv, Engine and DeepPlate. We implement the same functions as MODULES in one build, and go further with the frame pack, the sealed reading and the S.63(4) certificate.
Also evaluated, and not in the table
Any set of columns is a choice, so here is what this one left out rather than hiding it.
- Cellebrite and GrayKey. Locked and recent handsets. We run the public acquisition methods in-house and reach the modern frontier through a licensed capability seam that our agreements fill.
- X-Ways. A capable single-examiner platform tool with strong RAID and memory work in a tiny footprint. Left out of the columns to keep the table readable.
- Autopsy. Free and open source, on The Sleuth Kit. The right answer for a lab with no budget; no video forensics, no physical recovery.
Compared by capability category rather than feature by feature. Every mark was checked against the vendor's own published material, rechecked September 2026.
Where we are ahead
- Recovery and forensics in one product: an exhibit that turns out to need RAID reassembly, database extraction or ransomware triage does not have to leave the tool.
- RAID, NAS and storage-pool rebuild as a first-class capability rather than a manual disk-configuration dialog.
- Database-server recovery: tables and rows out of MDF, InnoDB, PostgreSQL, MongoDB and the rest. None of the four do this.
- Physically damaged media, through our own lab.
- An offline key with no cloud check, and a per-file verdict that states what could not be verified.
The same bench, on every endpoint
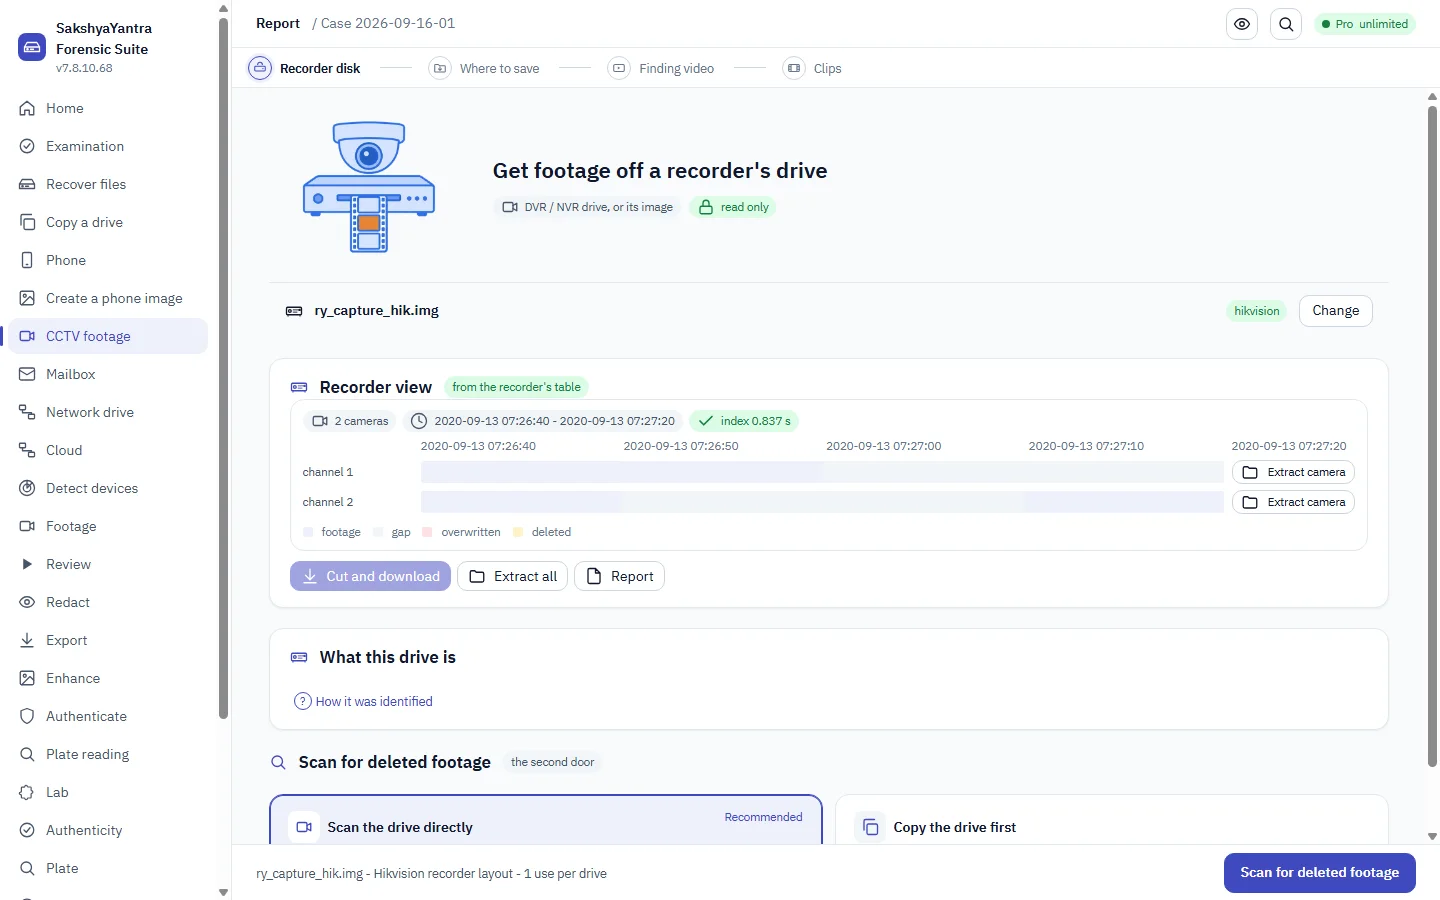
SakshyaYantra Forensic Suite carries an agent for the machines: sweep the estate for a filename, an exact SHA-256 or a string inside files, acquire a machine that cannot be switched off with its volume frozen at one instant, and queue the laptops that are away - with everything on this page underneath, in the same build.
Produce a case file that carries its own evidence
Image, hash, analyse and report with one tool, fully offline. Or hand the exhibit to our lab.